en


TRINETRA-SHAKTI
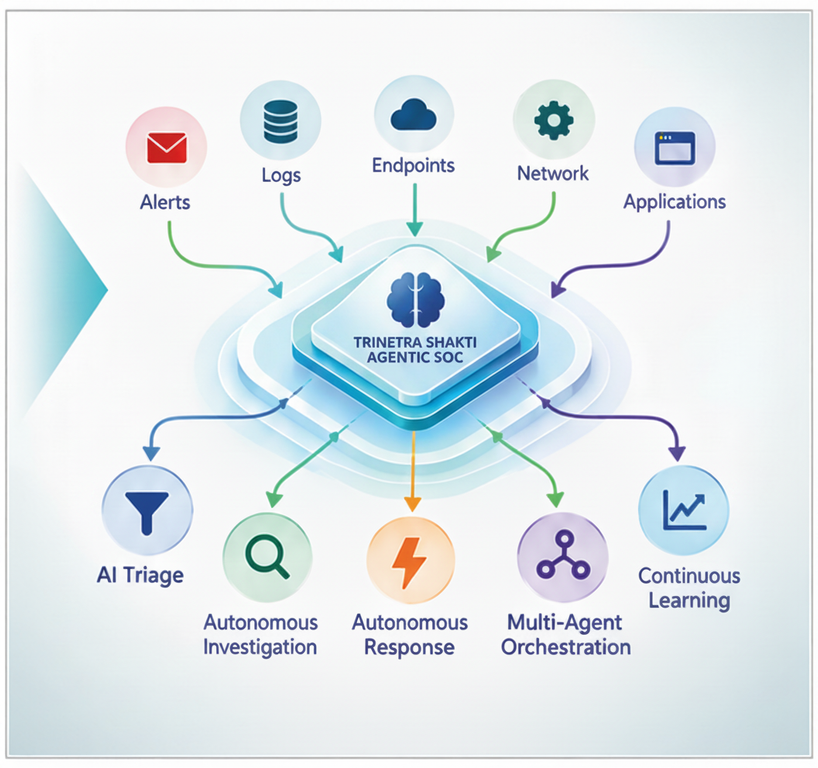
TRINETRA SHAKTI is a sovereign, indigenous Agentic Security Operations Center platform developed by C DOT that introduces multi agent workflows for autonomous cyber defense. Instead of replacing existing investments, it acts as an intelligent orchestration and reasoning layer above a security data lake, integrating telemetry from endpoints, networks, cloud, identities and traditional SOC tools. Traditional SOCs face alert overload, tool sprawl and manual processes, while attackers operate at machine speed. Moving to an AI SOC brings order and speed by prioritizing high risk signals, accelerating investigation, correlating evidence across sources and orchestrating actions, all with human oversight. Teams get fewer false distractions, faster detection and response, and better value from the tools they already own. This shift is a maturity journey. It begins by establishing a secure, scalable security data lake that unifies data from all relevant sources. The next step applies AI models and behavioral analytics to normalize data, learn baselines and surface meaningful anomalies; followed by introduction of agentic workflows: first as an assistant and co pilot to analysts, and progressively as governed automation where multi agent orchestration handles routine steps, maintains audit trails and seeks human approval for critical actions. TRINETRA SHAKTI is built to support this phased approach. It coexists with current controls, protects data sovereignty, and steadily advances SOC operations from human led to AI agent led, while remaining human governed throughout.
• Reasoning AI • Autonomous Investigation • Cross-domain Correlation • Autonomous Response • Attack-path Analysis • Continuous Learning • Human-in-the-Loop Governance • Massive Telemetry Sources • Unified Security Data Lake • Threat Intelligence Integration • Specialized Multi-Agent Framework